Key Attestation Demo

- 13.00 Reviews
- 4.8
- Downloads
- 100,000+
Our take on Key Attestation Demo from Appgk
Key Attestation Demo is the kind of Android app I would recommend only after understanding what you want to learn. It is not a general-purpose utility, a security scanner, or a tool that makes a phone visibly safer with one tap. Instead, it is a focused demonstration of the Android system’s Key Attestation feature, aimed at people who want to inspect how cryptographic key information can be presented and evaluated on a device.
That narrow purpose is also its biggest strength. Many security concepts are difficult to understand because they stay hidden behind libraries, APIs, and technical documentation. This app gives the subject a practical place to start. I found it more useful as a learning and testing companion than as an app I would open every day, but that is not a criticism of its design. It knows what it is trying to show, and the experience makes more sense once you stop expecting a conventional consumer app.
What the demo actually offers on a phone
Developed by Xingchen & Rikka, the app sits in the Libraries & Demo section rather than in a typical security or productivity category. That placement matters because it sets the right expectation: the application is primarily for exploring a system capability, not for replacing password managers, antivirus software, device diagnostics, or enterprise security tools.
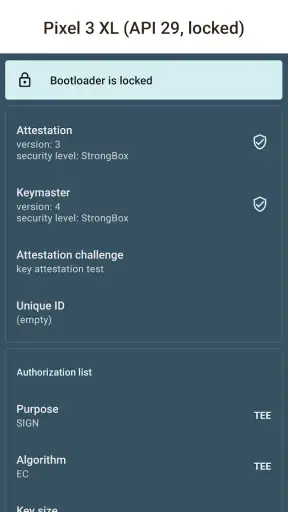
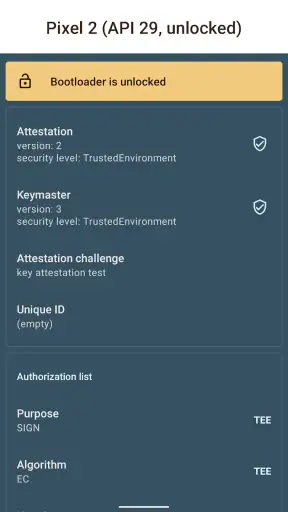
On a compatible Android device, the central experience revolves around Key Attestation. In practical terms, that means the app helps you examine information associated with cryptographic keys and the environment in which those keys are held. I would describe it as a visible demonstration layer for a subject that developers often encounter through code and technical references rather than through a friendly interface.
Best Parts of Key Attestation Demo
Things to Keep in Mind About Key Attestation Demo
The app is free, carries an Everyone age rating, and supports Android seven or later. Its current version is 1.5.0. Those details make it easy to try on an older supported phone, although support for the operating system alone should not be confused with identical behavior across every device. Key-related system capabilities can depend on the phone’s hardware, Android implementation, and security configuration, so the most useful results are always tied to the device being examined.
The listing shows a 4.8 average from over three hundred ratings, with more than one hundred thousand installs. I read those figures as a sign that the app has found a clear audience among Android enthusiasts and developers, rather than as proof that it will be useful to everyone. A high rating cannot turn a specialized diagnostic demonstration into a mainstream utility, and a newcomer should install it with the right goal in mind.
News and Features Related to Key Attestation Demo

News
YouTube Turns a Quick Video Check Into an Hour of Watching

News
BeautyPlus Makes Portrait Retouching Feel Like Your Own

News
TikTok’s Effortless Feed Makes Every Swipe Count—and Every Mistake Harder to Undo
Why the network connection is not the main event
The interesting parts of a Key Attestation demonstration are rooted in the relationship between the app, Android, and the device’s security environment. That makes this a different kind of experience from an app that constantly downloads articles, synchronizes notes, or streams content. You are not opening it for a feed that changes every minute. You are opening it to inspect a system-level result.
Even so, connectivity can shape the experience around the edges. If you are researching a result, checking terminology, comparing a device with another model, or sending information to a colleague, you may need a browser, documentation, messaging app, or another online resource alongside the demo. The app itself is therefore best understood as one part of a technical workflow, not as a complete explanation of every security field it displays.
Don't want to read the full review?
My practical advice is to decide what you are testing before launching it. If you are checking whether two phones expose different attestation behavior, record the model, Android release, and relevant result from each device. If you are learning the concept, keep a reference open separately and translate each technical item into a question: what is being attested, which part comes from the system, and what conclusion is actually justified?
The most important habit is to treat the output as evidence, not as a simple “safe” or “unsafe” verdict. A demonstration app can reveal useful technical information without making a complete judgment about the trustworthiness of a phone, an application, or a person using it. That distinction prevents a lot of overconfident conclusions.
Screenshots
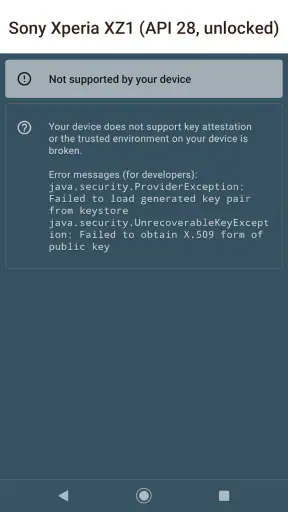
Useful mobile situations for a specialized demo
The app makes the most sense on a physical Android device when you are investigating that device’s own environment. A developer testing an authentication flow can use it as a quick companion while comparing behavior between a development handset and another phone. A student learning Android security can use it to connect abstract explanations of key attestation with something observable. An enthusiast who owns several devices can use it to understand why similar-looking phones may expose different security characteristics.
A realistic everyday scenario might look like this: you are helping a small team test an Android sign-in feature, and one tester reports that a security check behaves differently from yours. Instead of immediately blaming the network or rewriting the application, you open Key Attestation Demo on both phones, capture the relevant results, and compare the environments. You still need proper application logs and documentation, but the demo can help identify whether the devices are presenting different conditions before the team spends hours investigating the wrong layer.
Another useful situation is preparing a second-hand phone for development or testing. The app can give you a more technical view of the handset than a normal settings screen, which may help you understand why a security-sensitive experiment behaves differently after a reset, update, or change of device. I would not use it as the only basis for deciding whether to buy a phone, but it can be a helpful part of a broader inspection.
There is also value in using it while teaching. Instead of describing attestation as an invisible backend exchange, an instructor can let learners observe the kinds of information a system-level demonstration exposes and then discuss the limits of that information. That turns the app into a conversation starter. It is especially good for showing that security is layered: a key result is one piece of an architecture, not the entire architecture.
Where the mobile experience becomes less convenient
The phone form factor is both an advantage and a limitation. It is convenient because the app can examine the device in your hand, without requiring a separate computer for the initial inspection. At the same time, technical output can be harder to read, compare, or document on a small screen. When I am dealing with several fields or several test devices, a larger display and a written test plan become more valuable than the app alone.
This is also not the kind of application I would hand to a family member who simply wants reassurance that a phone is secure. The terminology and the purpose are too specialized for that use. Someone looking for a clear consumer-facing health check would be better served by the phone maker’s security settings, an account-security review, or a dedicated tool designed to explain risks in ordinary language.
Developers should also avoid turning a single observation into a universal compatibility rule. A result on one handset does not automatically describe every Android phone, and a change between two devices may reflect hardware-backed security, system configuration, software state, or the way a particular application requests and interprets attestation. The demo is valuable precisely because it encourages investigation, but it cannot remove the need for careful testing.
Handling confusing results and recovering from a dead end
The first recovery step is simple: do not assume that an unexpected result means the app has failed. With a system feature this specialized, an unfamiliar value may reflect the device or the Android environment rather than a broken interface. I would repeat the test after checking that I am examining the intended phone, noting the operating system version, and avoiding comparisons based only on memory.
If you are working with a team, write down the exact context of each observation. Record which handset produced it, whether the device had recently changed configuration, and what application or test flow led you to open the demo. This small discipline is more useful than repeatedly tapping the same screen without a question in mind. It turns the app from a curiosity into a reproducible investigation tool.
Connectivity can complicate recovery when the next step requires outside documentation or collaboration. If a result is unclear, you may need to look up Android terminology, consult a project’s security notes, or send a screenshot or written summary to another developer. That does not make the demo a network-first app; it simply means that technical interpretation often extends beyond the screen in front of you.
I would also avoid treating a failed or incomplete-looking test as a reason to install several unrelated security apps immediately. Extra tools can introduce more variables and make it harder to tell which result belongs to which layer. Start with the demo, the device context, and the official technical explanation of the feature. Add other tools only when you have identified a specific question they can answer.
A particularly useful advanced workflow is to compare observations before and after a controlled change rather than collecting random screenshots. For example, test one device, document the result, make one deliberate system or application change, and test again. The point is not to manufacture a favorable outcome; it is to learn which change appears to affect the attestation-related information. This approach produces much stronger evidence than comparing phones that differ in several ways at once.
Using it without wasting mobile data
For a data-conscious user, the app’s focused nature is reassuring. You are not dealing with a content-heavy library, video stream, or social timeline that demands constant downloads. The main value comes from the local interaction with Android’s security facilities, while online activity is more likely to happen when you search for explanations or share findings elsewhere.
That means the best way to conserve data is to separate testing from research. Run the demonstration when you have the device available, write down the important results, and postpone broad web searches until you have a clear list of terms to investigate. This is more efficient than repeatedly switching between the app and several online tabs while trying to remember what each field means.
If you are comparing multiple phones, keep a compact record rather than sending a full collection of screenshots through mobile messaging. A short note with the device identity, system context, and relevant observation is easier to review and uses fewer resources. Screenshots still have a place when visual evidence matters, but they should support a conclusion rather than replace one.
I would not install this app solely because it is small, free, or popular. Its usefulness comes from the question behind it. If you are curious about Android’s key security mechanisms, building an authentication feature, teaching mobile security, or diagnosing a device-specific difference, the focused design is a benefit. If you simply want an app that improves battery life, blocks threats, stores passwords, or explains privacy settings, this is the wrong category of solution.
How it compares with ordinary alternatives
Compared with a standard device-information app, Key Attestation Demo is narrower but potentially more meaningful for security-focused testing. General hardware tools may show the processor, memory, sensors, and software build in a convenient summary, yet they are not designed around the specific question of Android Key Attestation. They are better for a broad inventory; this demo is better when the cryptographic and trust-related layer is the subject.
Compared with a consumer security suite, the difference is even clearer. A security suite may focus on suspicious files, harmful applications, browsing protection, or account alerts. Key Attestation Demo does not occupy that role. It is closer to a technical inspection window than a protective shield, so choosing it as an antivirus replacement would lead to disappointment.
Compared with reading documentation alone, the app offers a more concrete starting point because it puts the concept on an actual handset. Documentation remains the better source for definitions, implementation details, and correct interpretation, while the demo supplies the device-specific observation. I see the two as partners: the app gives you something to examine, and the documentation helps you avoid reading too much into it.
Compared with writing your own small test application, this demo is a faster first step for someone who wants to explore the feature without building an interface and handling the initial plumbing. A developer with very specific requirements may eventually need a custom test harness, especially when integrating attestation into a larger authentication design. For learning, comparison, and preliminary investigation, however, a ready-made demonstration is less friction.
Who should install it, and who should skip it
I would recommend it to Android developers working with authentication or device trust, students studying mobile security, testers comparing handsets, and technically curious users who enjoy understanding what their phone exposes beneath the usual settings screens. The free price makes experimentation easy, and the Everyone rating means the app is not presented as age-restricted content.
I would skip it if your goal is immediate protection, a simple privacy score, a battery diagnosis, or a friendly explanation of whether your phone is “secure.” The app’s specialized subject is likely to feel confusing rather than helpful in those cases. I would also skip it if you have no concrete question and do not want to spend time learning what the displayed information means. A technical demo is most rewarding when curiosity is paired with a practical purpose.
Before installing, ask yourself three useful questions. Am I examining a particular Android device rather than looking for a general security service? Am I willing to verify the meaning of technical results instead of relying on a single label? Do I have a workflow for recording and comparing observations? If the answer to those questions is yes, the app has a much better chance of earning a place in your toolkit.
My final view on its connected, practical value
After using Key Attestation Demo as a focused technical companion, I see it as a strong example of an app that does not need a broad feature list to be useful. Its value lies in making Android’s Key Attestation feature easier to approach on a real device. The experience is not built around constant connectivity, and that is welcome: the central task is inspection, while online research and collaboration support the work around it.
Its limitations are tied to the same specialization that makes it worthwhile. The information can require careful interpretation, results may vary with the device and system environment, and the small-screen format is not ideal for extended comparison. None of those points makes the app poor; they simply define the kind of user who will benefit from it.
For me, the best way to use it is deliberately: choose one question, inspect one device, record the context, compare only controlled changes, and consult reliable technical material before drawing a conclusion. Used that way, Key Attestation Demo is more than a curiosity. It becomes a practical bridge between Android security theory and the behavior of the phone in your hand.
My recommendation is therefore positive but specific. Install it if you want to explore Key Attestation, troubleshoot a security-sensitive Android workflow, or learn how device-level evidence fits into a larger authentication design. If you want a protective everyday app, choose a tool made for that job instead. For the right audience, this free demonstration earns its place by being focused, transparent about its purpose, and useful without pretending to be a complete security solution.
Key Attestation Demo FAQ
What is Key Attestation Demo, and what is it used for?
Key Attestation Demo is an Android utility designed to demonstrate how hardware-backed key attestation works through the Android Keystore system. It can help developers, security researchers, and advanced users inspect whether cryptographic keys are protected by secure hardware, such as a Trusted Execution Environment or StrongBox, when supported by the device. It is primarily an educational and testing tool rather than a general-purpose security app.
Does Key Attestation Demo work on every Android device?
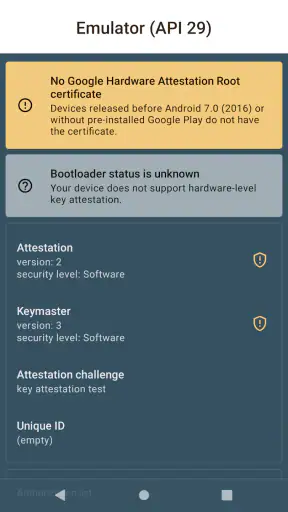
The application may install on many Android phones and tablets, but the information it can display depends heavily on the device model, Android version, manufacturer implementation, and available security hardware. Older devices may provide limited attestation data or no hardware-backed support at all. Results can also differ between physical devices and emulators, so the app should not be used to assume that every Android device offers the same level of protection.
Does using Key Attestation Demo root my phone or change its security settings?
Key Attestation Demo is generally intended to inspect Android’s key attestation capabilities without requiring root access or modifying system files. Running a test should not unlock the bootloader, install a custom recovery, or alter your device security configuration. However, users should download the application from a trustworthy source and review the permissions requested. If your device is rooted, modified, or running unofficial firmware, the displayed results may be less reliable.
What do hardware-backed, StrongBox, and verified boot results mean?
The terminology shown by Key Attestation Demo can be technical. Hardware-backed usually indicates that key operations or attestation information are protected by a secure environment rather than handled entirely by normal Android software. StrongBox refers to a more isolated security component available on some devices. Verified boot information can indicate whether the operating system has passed integrity checks. These results are useful indicators, but they are not a complete security audit.
Is Key Attestation Demo safe to use, and does it collect personal data?
The app is designed for local testing of Android security features, so its main purpose should not require access to contacts, messages, photos, or account information. Nevertheless, privacy depends on the specific version and its developer, so check the store listing, requested permissions, privacy policy, and any network activity before installing. Avoid entering confidential information, and remember that an attestation result alone does not guarantee that the entire device or every installed app is secure.